AppCraft.Africa
Software, AI & cyber-defence studio · KE · NG · TZ · ZA

We build software for fintech & insurance in Africa.

AppCraft is a senior engineering studio — 14 years, 400 + products, four continents — now focused on Africa's financial sector. We build the core systems, customer apps and applied AI that banks, insurers and fintechs run on, and we defend them: identity, fraud detection, and security for the AI itself. Built so that no single AI vendor can hold you hostage, and delivered as fixed-scope modules your risk team can sign off.

Fintech & insurance focus
Vendor-agnostic — you keep the keys
On the ground in East Africa
14
years

One engineering team, working together since 2011

400+
products

Delivered across four continents

100+
engineers

In-house — design, backend, machine learning, security

5
ventures

Past $2m revenue; one acquired by a tier-one telecom operator in 2025

3
regulated regions

Banks, insurers, telecom and government across the CIS, the Gulf and South-East Asia

4
African markets

KE · NG · TZ · ZA — on the ground, on local time

Headquartered in Tbilisi, Georgia. We build and operate — we do not resell.


Why now

The numbers are already on the table.

Two forces move at once. The value of AI here sits in applying models, not in building them — and the crime built on those same models is growing faster in Africa than almost anywhere. Both are measured. Supervisors have started pricing the second one.

0.6%

Africa’s share of the world’s data-centre capacity, with about 18% of the world’s people. The compute gap will not close this decade.

Africa Data Centres Association, 2026

$2.9 tn

Value AI could add to Africa’s economy by 2030 — almost all of it from applying models, not from building them.

GSMA, AI for Africa

55%

Of all reported cybercrime in Africa in 2025 was AI-enabled. That is now the normal case, not the exotic one.

INTERPOL Africa Cyberthreat Assessment, 2026

$5 bn

Direct economic losses across Africa in 2025. Reported financial losses rose 152% year on year.

INTERPOL Africa Cyberthreat Assessment, 2026

+393%

Rise in Africa’s deepfake fraud rate in a single year — the second-fastest-growing region in the world.

Sumsub Identity Fraud Report

44 of 55

African countries with data-protection laws in force. Several require a regulated institution’s primary data to stay in the country.

Digital Policy Alert

The regulator is already moving

Five markets, five sets of penalties, one direction.

Market Penalty exposure today What supervisors now require
Nigeria ₦10m or 2% of revenue CBN Risk-Based Cybersecurity Framework 2024. A ₦766m fine was issued in 2025.
Kenya KSh 5m or 1% of turnover CBK cybersecurity guidance. Over 110 enforcement decisions issued in 2025.
South Africa R10m and up to 10 years SARB and FSCA Joint Standard 2 of 2024.
Rwanda 1–5% of turnover, plus prison BNR regulation. A bank’s primary data must stay in Rwanda.
Tanzania TZS 100m, plus criminal Bank of Tanzania draft guidelines: board-approved strategy, annual penetration tests, 24-hour reporting.

All five move the same way: strong authentication, privileged-access control, tested defences, 24-hour reporting — each one a line item we deliver. Sources: CBN Risk-Based Cybersecurity Framework 2024 · CBK guidance · SARB and FSCA Joint Standard 2 of 2024 · BNR regulation · Bank of Tanzania draft guidelines. Exact penalties are governed by the regulation in force in each jurisdiction.

What we do

Everything above the model, under one contract.

We build the AI systems and the software around them, defend the institution that runs them, defend the AI itself, and prove the defence by attacking it. Eight lines of work, engaged module by module and priced per scope.

AI engineering & transformation

Custom AI systems, and the operating layer under them

Large companies no longer buy AI tools; they build an internal layer that connects their documents, systems and processes, and run narrow assistants on top of it. We build that layer for African institutions — with agents that have a measurable job, not a chatbot that impresses in a demo and dies in production.

  • Retrieval over your own knowledge, agent workflows, domain testing
  • Process redesign — the work rebuilt around the model, not bolted onto it
  • Cost and accuracy budgets, data-governance rules, a written AI policy
  • Hands-on enablement for the people who use it every day
Software & mobile engineering

Complex systems, built and integrated

The bench that carries AI into production, and that ships everything around it. Native mobile, web, backend and core-system integration for banks, insurers and fintechs — delivered as fixed-scope modules your risk team can sign off.

  • Integrations & APIs — M-Pesa Daraja, PesaLink, core banking
  • Claims, underwriting & onboarding tooling
  • Embedded finance & bancassurance distribution
  • Mobile, web & USSD customer surfaces
Cyber defence & identity

Who gets in, what they may touch, and proof of both

The strong authentication central banks now require, since one-time SMS codes no longer count. Multi-factor and biometric login, single sign-on, control of privileged accounts with session recording, certificates and public-key infrastructure, and identity threat detection that watches the accounts themselves.

  • Privileged access, session recording, third-party vendor access
  • Certificates and public-key infrastructure
  • Hardware tokens, smart cards and biometric readers — issued, managed and revoked in one place
AI-era KYC & media forensics

Detection for generated faces, voices and documents

Our own detectors for generated and edited images, cloned voices and forged financial documents — wired into onboarding, lending, claims and the call centre, on your premises or as an API. Every model is paired with human review, and we never promise a fixed catch rate.

Live — free to try, no sign-up

Security for your AI

The AI you deployed is a door nobody is watching

Access control on models, defence against prompt injection, removal of personal data before anything leaves the perimeter, discovery of the shadow AI your staff already use, a full audit record of every model call, and an AI governance policy your regulator can read.

97% Of the organisations that suffered an AI-related security incident had no proper access controls on their AI.

IBM Cost of a Data Breach, 2025

Offensive audit & drills

We attack you before someone else does

Penetration testing, red-team exercises and a deepfake drill against your own executives and call-centre staff — so the first synthetic voice they hear is ours, not a criminal’s. We will also audit a defence somebody else built and sold you.

  • Generated video and voice of your own executives, on your own channels
  • Forged documents through your real onboarding and claims path
  • Prompt attacks against the AI you already run
Compliance monitoring

Automated compliance monitoring

We do not sell compliance advice — we build the system that watches it for you. Automated checks against the rules that apply to your sites, products and AI assistants, plus continuous tracking of regulatory change in each market you operate in.

  • Conformance scans for sites, products & AI assistants
  • Legislative-change monitoring, per market
  • Drift alerts mapped to your obligations
Sovereign deployment

Inside your perimeter, under your country’s law

On-premise, in-country cloud or hybrid, designed around the data-protection law of your market rather than retro-fitted to it after the audit. Outside vendors are used to check and validate results — never to hold your customer data.

  • Open-weight models on your own hardware for regulated data
  • Deployment designed per market, before the proposal is written
  • Handover: the system, the runbook and the reasons behind both

How we build

Two mechanisms we do not compromise on.

One governs how AI touches your data. The other decides whether your defence is real. Both are design rules, not options on a price list.

01

Split the work, keep the keys

Several AI vendors do the computing. None of them ever sees enough to reconstruct your business. The router that decides who sees what sits inside your perimeter and belongs to you.

Your perimeter — on-premise or in-country

Your data

customers · claims · documents

Keys & identities

never leave this box

The router — yours, not a vendor’s

splits each task · strips identifiers · picks the model · rejoins the answer

Private models on your own hardware

open-weight models for anything touching personal data

Only fragments leave the perimeter

Vendor A

sees fragment 1 — no identifiers, no context

Vendor B

sees fragment 2 — cannot join it to fragment 1

Vendor C — the checker

re-checks the answers of A and B

Answers come back and are rejoined inside the perimeter.

01

No vendor sees the whole picture

Every task is broken into parts before it leaves your network. Each provider receives only the fragment it needs. Names, account numbers and the logic that joins the parts back together stay inside. A leak at any one vendor exposes a fragment, not a customer.

02

The router belongs to you

A model-neutral layer picks the provider for each task by cost, quality and legal residency. Replacing a vendor is a configuration change, not a rebuild. Prices move, providers fail, rules change — your system keeps running.

03

Sensitive work never leaves

Anything touching personal or regulated data runs on open-weight models on your own hardware or in-country cloud. External providers are used only where sending data out is safe and lawful.

04

A cheap worker, an expensive checker

A fast, low-cost model does the volume. A stronger, independent model checks the result. Two different vendors have to be wrong in the same way before a bad answer reaches a person.

02

Red team against blue team, in permanent competition

One of our teams builds and defends. The other attacks the same system with the tools a real attacker uses today — generated video and voice of your own executives, forged documents, stolen credentials, prompt attacks against your AI. You can hire either side, or both, and you can have your existing supplier audited from the attacking side.

Red team — attacks

Breaks in the way an attacker would

deepfakes your executives · clones voices · forges documents · breaks the login · injects prompts into your AI

Your system

Audited from both sides

identity · channels · call centre · onboarding · payments · your AI

Blue team — defends

Closes what the other side opened

detection · identity controls · response · monitoring · governance

What the attacking team finds on Monday becomes a working detection on Friday.

Defence that has never been attacked is an opinion, not a control.

Your team

We do not replace your people. We build centaurs.

A centaur team is a person and a machine working as one unit, each doing what it is good at. It is not a slogan — it is the best-measured result in the field. It only works when someone designs the line between the two, and that design is the work we do.

+25%

Faster work, 12% more tasks completed and 40% higher quality, when professionals used AI inside the range it is good at.

Harvard/BCG field experiment, Organization Science, 2026

+19 pts

More likely to be wrong when the same people used it outside that range. Drawing that boundary is the whole job.

Same study

+34%

Productivity gain for junior staff across 5,179 support agents, against +14% on average. AI lifts the inexperienced most.

Brynjolfsson, Li and Raymond — field study

The last number is the one that matters here.

The developer pool across the continent is large and young, and senior specialists are hired away offshore faster than they can be replaced. AI lifts the inexperienced most. A centaur design turns a junior team into a mid-level team — and it closes that gap faster than hiring can.

What that looks like in practice

  • We map where the model is reliable and where it is not, then build the boundary into the tool itself.
  • Hands-on training for the people who use the system daily, and for the managers who have to trust its output.
  • Your team keeps the work. We hand over the system, the runbook and the reasons behind both.

Full-cycle engineering

One team for the whole build — apps, AI and the systems under them.

Build, detection, identity and governance under one agreement — not four procurements that blame each other when something fails.

Apps & front-ends

Mobile & web products, shipped to the store

iOS, Android and web — from problem statement to a live, maintained product. Offline-tolerant, localised, built to survive real users.

AI & LLM systems

Applied AI your risk team can approve

Retrieval, multi-step pipelines, computer vision and the fraud models behind our own detectors — built to be evaluated, monitored and handed over.

Backend, cloud & APIs

Systems & infrastructure that hold up

Scalable backends, data pipelines and clean APIs — including the production endpoints that serve our detectors at volume.

Our LLM Playbook

Four patterns that turn AI demos into things your business runs on.

Most failed AI projects fail the same way: the prototype works on a slide and dies under real load, real costs and real edge cases. Our work starts where the demo stops.

01 Production

Multi-step LLM pipelines

Long-running jobs broken into deterministic steps, each with its own model, prompt, retry policy and evaluator. The cheapest model that can do the step does the step.

  • Document → extract → classify → enrich → review
  • Per-step cost & accuracy budgets
  • Replay-able runs for audit
02 Production

Retrieval-Augmented Generation (RAG)

Domain knowledge stays in your systems. The model sees only the relevant passages, with citations the user can verify.

  • Hybrid retrieval (BM25 + embeddings)
  • Source-grounded answers w/ citations
  • Permission-aware filtering
03 Production

RPA + LLM hybrids

Reading screens, structured forms and weird internal portals. The LLM decides; deterministic glue clicks the buttons. Works where the API does not exist.

  • Headless browser orchestration
  • Vision-language fallback for legacy UIs
  • Human-in-the-loop for risky steps
04 Production

Conversational interfaces

Internal copilots, agent-assist for support, customer-facing assistants — designed to fail gracefully and escalate to a human at exactly the right moment.

  • Tool-use with typed function schemas
  • Persona, tone & safety boundaries
  • Quality monitoring on every turn

Pilot blueprints

Three pilots we can start within a month.

Each one is scoped to win an internal reference, not to bill a large first invoice. Fit, sequencing and price depend on your data and the teams involved.

Get a tailored quote
Banking · Tanzania

Compliance-grade customer copilot

A copilot for front-line bank staff that answers product, KYC and policy questions with cited source paragraphs — and quietly escalates anything regulated to a human reviewer.

RAG over policy & product docs
Audit trail per answer (who asked, what was retrieved)
Prompt-injection & data-leak hardening
4–6 week pilot, scoped per-team
Lending · Nigeria

Underwriting & document-fraud pipeline

A pipeline that turns scanned application files and bank statements into structured, score-ready features — with our financial-document detector flagging forged statements and edited receipts before they reach the risk model.

OCR + extraction + verification chain
Confidence scores per field, human-in-loop UI
Hooks into your scoring engine
Outcome SLA on extraction accuracy
Insurance · South Africa

Claims triage & agent-assist

Fast-lane triage for incoming claims (drafted summaries, missing-info checks, fraud hints) with an agent-assist sidebar for the human handler. Designed for POPIA-shaped guardrails.

Triage classifier + summarizer
Agent-assist suggestions, never auto-decisions
PII redaction & retention policy enforcement
A/B against your current handle-time baseline

How we start

01

A working session

Two to three hours with the people who own the process, the identity stack or the exposed channel. We find where this pays, and where it does not.

02

One pilot, or one drill

One process in your environment, on your hardware — or a controlled attack on one channel. Small, real, finished in weeks.

03

A written page in 7 days

What we agreed, what we did not, and what we recommend you do not spend money on. No fine print.

Selected work

From global enterprises to East Africa’s banks & exchanges.

Different regions, different industries, the same engineering bar — now pointed at Africa's financial sector. We didn't start with LLMs; we got there after a decade of shipping things people pay to use.

Alongside these: NDA-anonymised consulting for a GCC financial group, and delivery for banks, insurers, telecom operators and government bodies across the CIS, the Gulf and South-East Asia — markets with strict supervision, data-residency rules and on-premise requirements. The same discipline African regulators now ask for.

Tanzania · Banking Banking systems

I&M Bank — Tanzania

A range of custom technical solutions for the Dar es Salaam arm of a regional banking group — built and delivered with our on-the-ground East African partner.

Tanzania · Capital Capital tech

Dar es Salaam Stock Exchange

Custom technical solutions for East Africa’s national stock exchange in Dar es Salaam — delivered with our regional partner, on local time.

Asia · Insurance Enterprise mobile

AXA — Malaysia

A field-agent companion app integrated with policy data and quote tooling for a global Tier-1 insurer. Mobile-first, offline-tolerant.

EU · Industrial B2B platform

TechnoNikol — global

B2B portal and internal tooling for a global building-materials manufacturer operating across dozens of markets. Multi-language, role-based, audited.

EU · Funded venture 0 → 1 venture build

Treeps — DE/NL

Marketplace platform that closed €250K from German and Dutch venture investors. Built from problem-statement to first live transactions.

Acquired Operator-led exit

Gymmy — fitness-tech

A fitness platform we co-founded and grew past $650K in revenue, acquired by a Tier-1 telecom operator in 2025. End-to-end product, ops & growth.

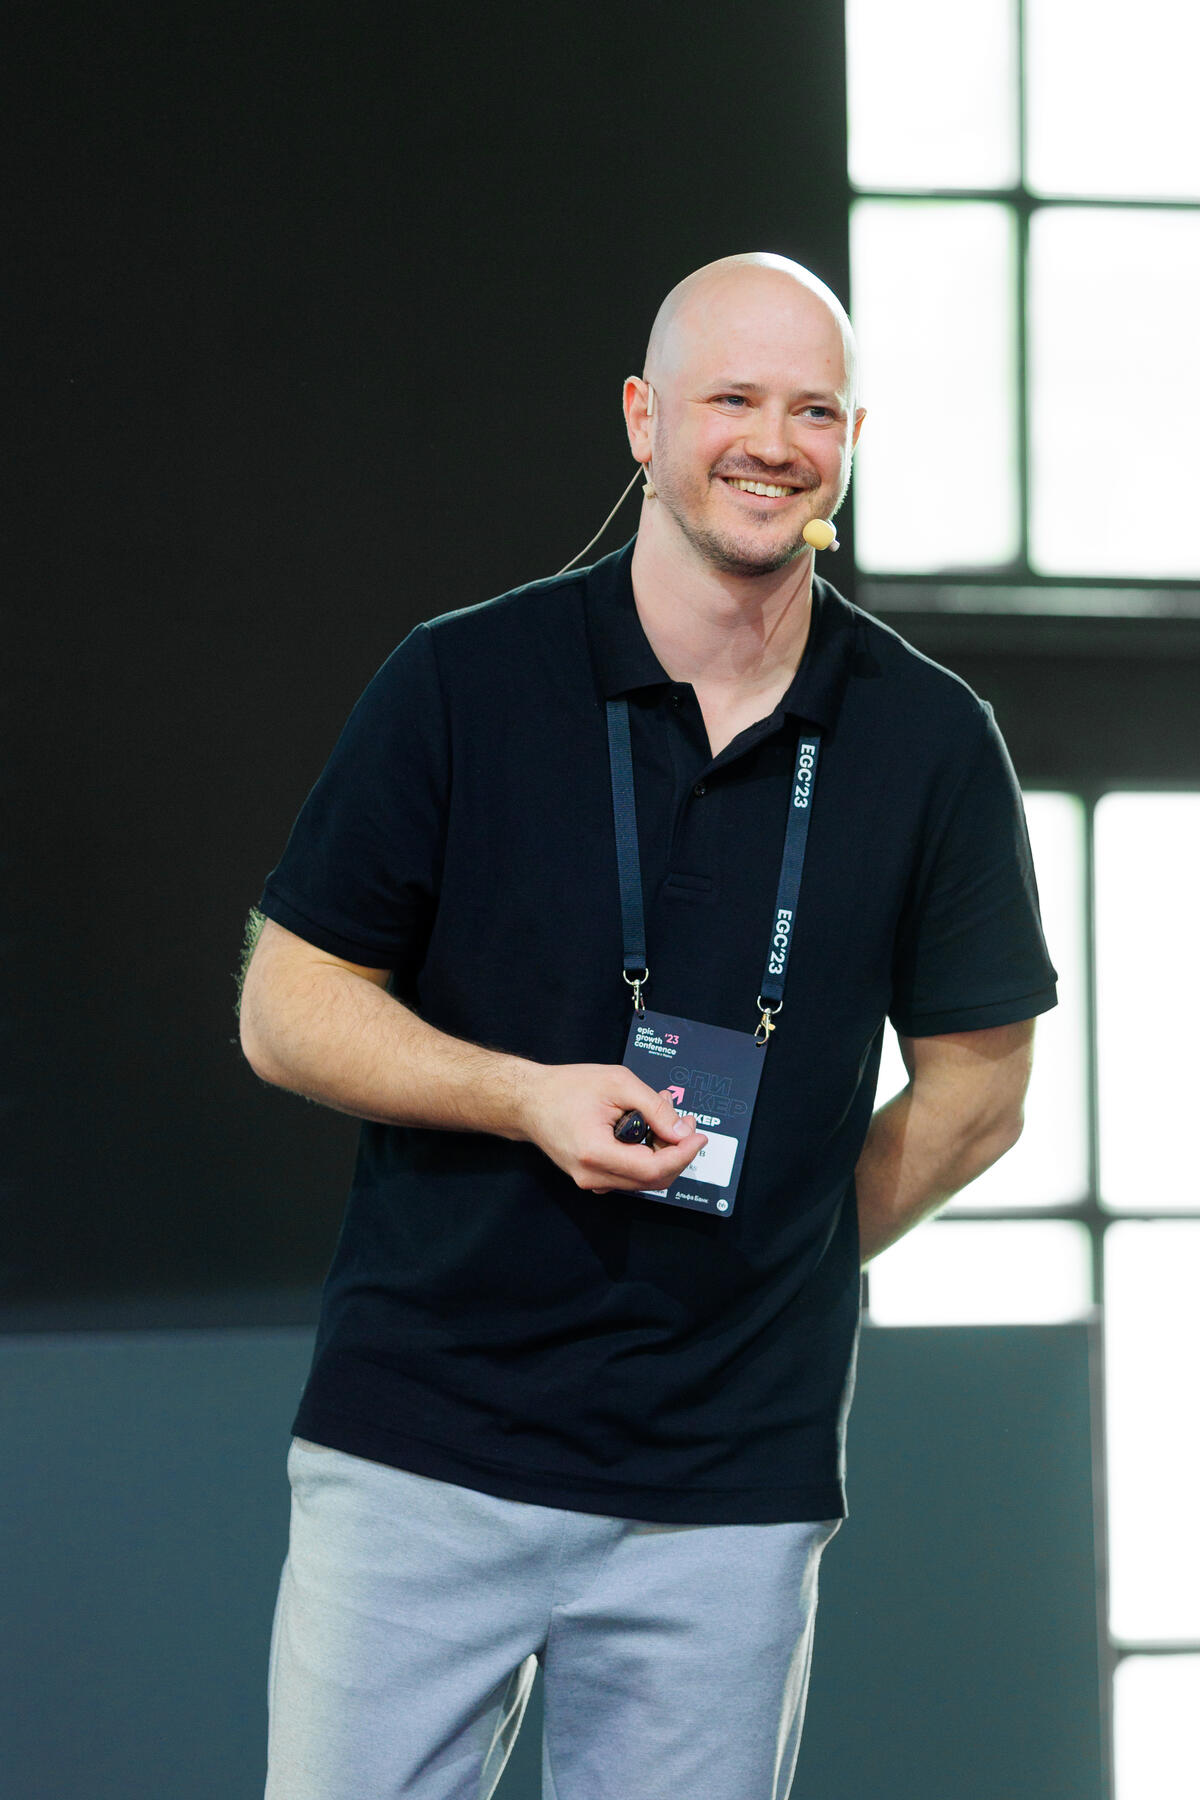
Alex — founder of AppCraft, on stage with a headset microphone.
Alex — speaking at a tech conference, EU

Founder

Hi — I'm Alex.

I've been shipping software since 2011. Built and ran the team that took 400 + products live across Asia, Europe, the Middle East and the Americas. I co-founded ventures past $2M in revenue and had one acquired by a Tier-1 telco in 2025. I'm the founder AppCraft Africa is built around.

I travel to the markets we serve — meeting customers in person, listening to their teams, and shaping pilots that fit the way local operations actually work. If you're a CIO, CTO or Head of Innovation in Kenya, Nigeria, Tanzania or South Africa, I'd genuinely like to hear what you're working on.

I read every direct message myself — no SDR layer, no auto-responses. A reply can take a little while when I'm travelling, but I try to give every thoughtful message a real, considered answer.

A note before we ask for your time

Hello — in the languages we're learning.

Every market has its own ways of saying it. We're here because we want to do the work properly — that starts with showing up, listening, and getting the small things right.

Jambo

Swahili · hello

Karibu

Swahili · welcome

Habari

Swahili · how are you

Mambo

Swahili · what’s up

Sawubona

isiZulu · I see you

Molo

isiXhosa · hello

Dumela

Setswana / seSotho · hello

Hallo

Afrikaans · hello

Our promise: we'll keep learning. We won't keep performing. And the basics of spotting synthetic media — we're putting into free explainers, in the languages of the markets we serve. That's also why our inbox is am@appcraft.pro.

What we don’t do

Things we don't promise — so we can deliver the things we do.

What we have learned in the field

The barrier is trust, not accuracy.

People forgive human mistakes and refuse to forgive machine mistakes. We have watched organisations stop a working pilot because the model was wrong 0.5% of the time — while the humans it replaced were wrong around 6.5%. Twelve times better, and still rejected. The barrier is psychological, not technical, so it has to be designed for.

AppCraft delivery experience, not a published study.

So we design for it

  • Output a person can explain to someone else
  • A named human who signs the decision
  • A clear audit trail — who asked, what the model saw, what it answered
  • An override that takes one click and no meeting

Systems built this way survive their first bad week.

We don’t train foundation models from scratch.

We use the world’s best models as interchangeable parts, and we never let one of them become a foundation you cannot remove.

No “proprietary AI platform” lock-in.

The router is yours. Your data and workflows stay in your systems, and anything we build is yours to own, audit and operate after handover.

No guaranteed accuracy or catch-rate numbers in a slide.

We define one or two measurable outcomes per pilot, instrument them and report against them honestly — including when they miss. Every detection model is paired with human review.

No surprise token bills.

Cost is a first-class design constraint, not a post-mortem. A cheap model does the volume, a stronger one checks it, and the budget is set before we write production code.

Straight answers

The questions we get asked first.

No sales language, no conditions hidden in a footnote. If an answer here rules us out for your case, that is the answer doing its job.

What does AppCraft Africa do?
AppCraft is a software and AI engineering studio working with banks, insurers, fintechs, telecom operators and government bodies in Africa. It delivers four things under one contract: custom software and core-banking integration; AI systems built inside the client’s own perimeter; cyber defence, identity and AI security; and automated compliance monitoring. AppCraft builds and operates what it sells rather than reselling another vendor’s product.
Which countries does AppCraft Africa work in?
AppCraft works across Kenya, Nigeria, Tanzania and South Africa, and takes engagements elsewhere on the continent. It is headquartered in Tbilisi, Georgia, and has delivered for regulated institutions across the CIS, the Gulf and South-East Asia — markets with strict supervision, data-residency rules and on-premise requirements comparable to those African regulators now apply.
Can AppCraft deploy AI inside our own perimeter, on-premise?
Yes. AppCraft designs for sovereign deployment as the default rather than the exception: on-premise, in-country cloud or hybrid, shaped around the data-protection law of the client’s market. Anything touching personal or regulated data runs on open-weight models on the client’s own hardware. By the end of 2025, 44 of 55 African countries had data-protection laws in force and several require a regulated institution’s primary data to stay in the country.
How does AppCraft avoid locking a client into a single AI vendor?
AppCraft builds what it calls a vendor-agnostic router: a model-neutral layer that belongs to the client, splits each task before it leaves their network, strips identifiers, picks a provider by cost, quality and legal residency, and rejoins the answer inside the perimeter. No single AI vendor ever sees enough to reconstruct the business, and replacing one is a configuration change rather than a rebuild.
Can we try AppCraft’s fraud-detection technology before committing?
AppCraft’s image-forensics detector is free and public at appcraft.africa/fake-image-detector/ — it checks a photograph for AI generation, deepfake face-swaps and editing, with five checks per hour per visitor and no sign-up. The voice-clone and forged-document detectors are built and deployed but are not public sandboxes: they run inside a client’s perimeter on the client’s own material, and AppCraft demonstrates them live on a call.
How much does an AppCraft engagement cost and how does it start?
AppCraft quotes per engagement rather than from a price list, because scope in regulated environments varies too widely for a published figure to be honest. It starts the same way every time: a two-to-three hour working session with the people who own the process, then one small pilot on one process in the client’s own environment, then a written page within seven days stating what was agreed, what was not, and what changes next.
What accuracy does AppCraft promise for deepfake and document detection?
AppCraft does not promise a fixed catch rate, and treats any vendor that does as a warning sign. Its detectors are risk screeners that stack several independent forensic vectors, return an explainable score rather than a verdict, and are designed with a human who signs the decision and an easy way to overrule the machine. A determined forger can defeat any single screener, which is why AppCraft runs several layers rather than one.
How do I contact AppCraft Africa?
By email, at am@appcraft.pro. There is no contact form and no ticket queue: mail reaches the founder directly and is usually answered within one working day. A first email is most useful when it says who you are, which process you want to change, which systems it touches, and what constrains you — a regulator, a data-residency rule, an on-premise requirement or a date.
Something here not covered? Write to am@appcraft.pro and ask it directly.

Start a conversation

Tell us what you're trying to build.

Write to us directly. Real briefs from real teams get a real reply — usually within one working day, written by Alex personally. No discovery-deck obligations. No follow-up SDR sequences.

Founder-direct email

am@appcraft.pro

Write to leadership

Alexander Murzanaev on LinkedIn

Meet in person

Kigali · Nairobi · Cape Town · Dar es Salaam

Write one email. That's the whole process.

There is no form to fill in and no ticket queue behind it. Mail goes straight to the founder's inbox. Four things make the first reply useful instead of generic:

  • 01

    Who you are

    Your role, your institution and the market you operate in.

  • 02

    The process you want to change

    Claims, onboarding, lending, the call centre, an internal workflow — and what is wrong with it today.

  • 03

    What it touches

    Core banking, payment rails, an existing vendor, a data warehouse. Rough is fine.

  • 04

    Your constraints

    The regulator, data residency, an on-premise requirement, a date you have to hit.

Email am@appcraft.pro

Opens your mail app with a short template already filled in. Prefer to write it yourself? Just send it to am@appcraft.pro.

We use what you send only to reply to you. No newsletter sign-up, no third-party sharing — see our privacy note. Under NDA before you send anything sensitive? Say so in the first line and we will send ours back the same day.